An Agent Exceeds Its Authorized Scope: Downgrade It or Stop It?
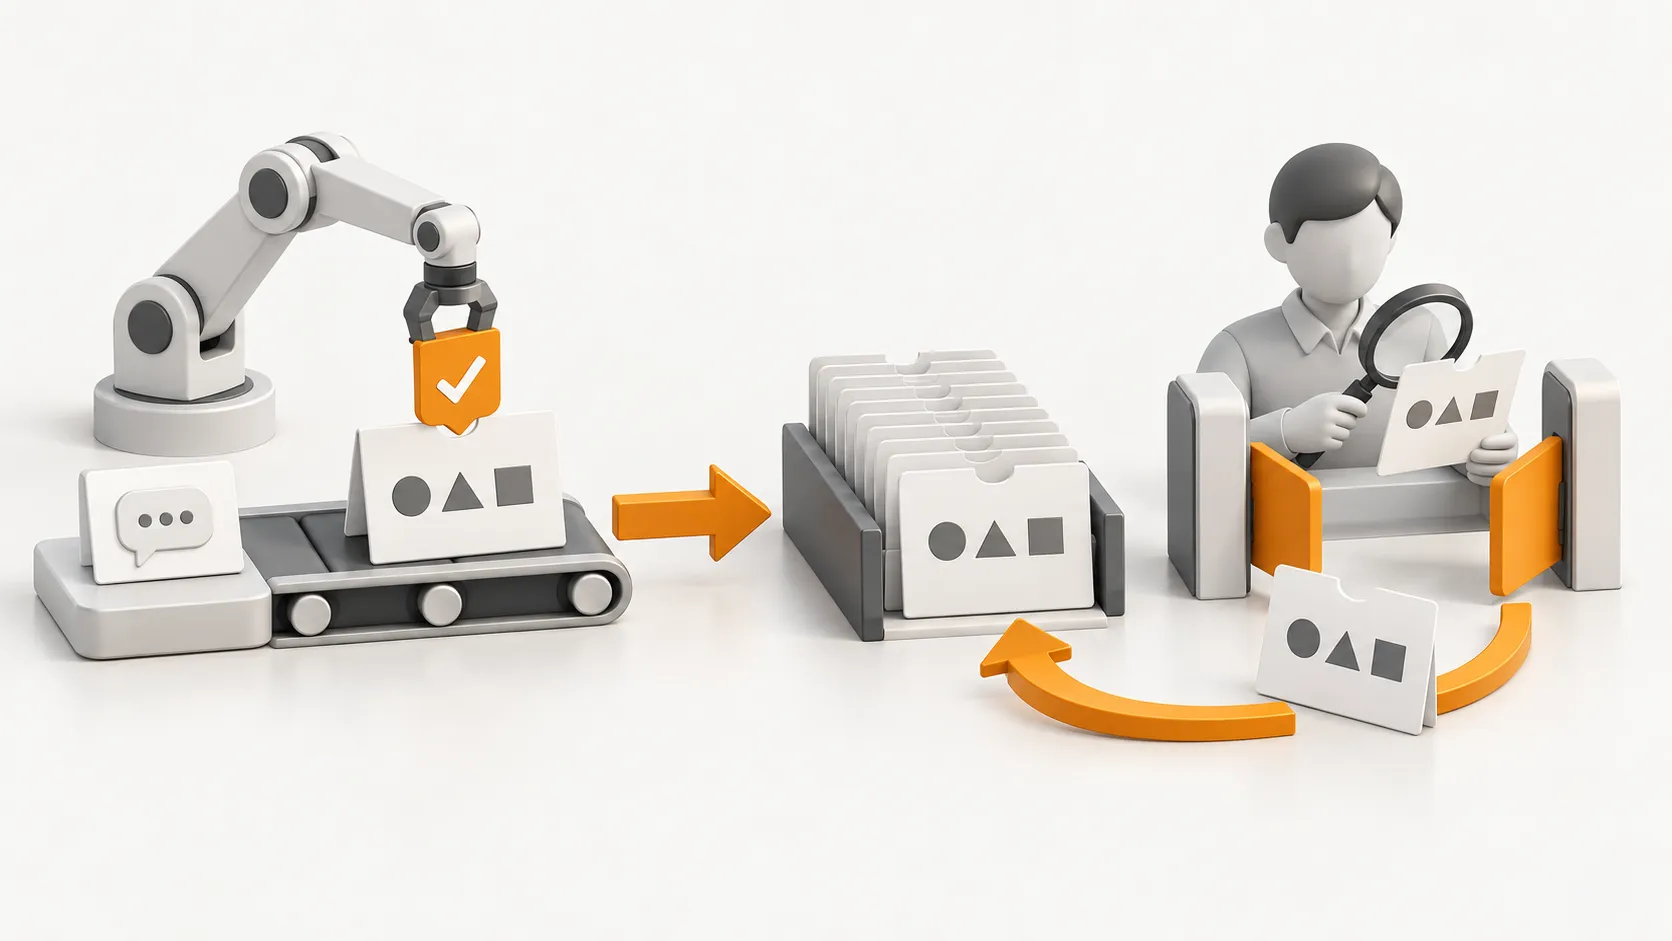
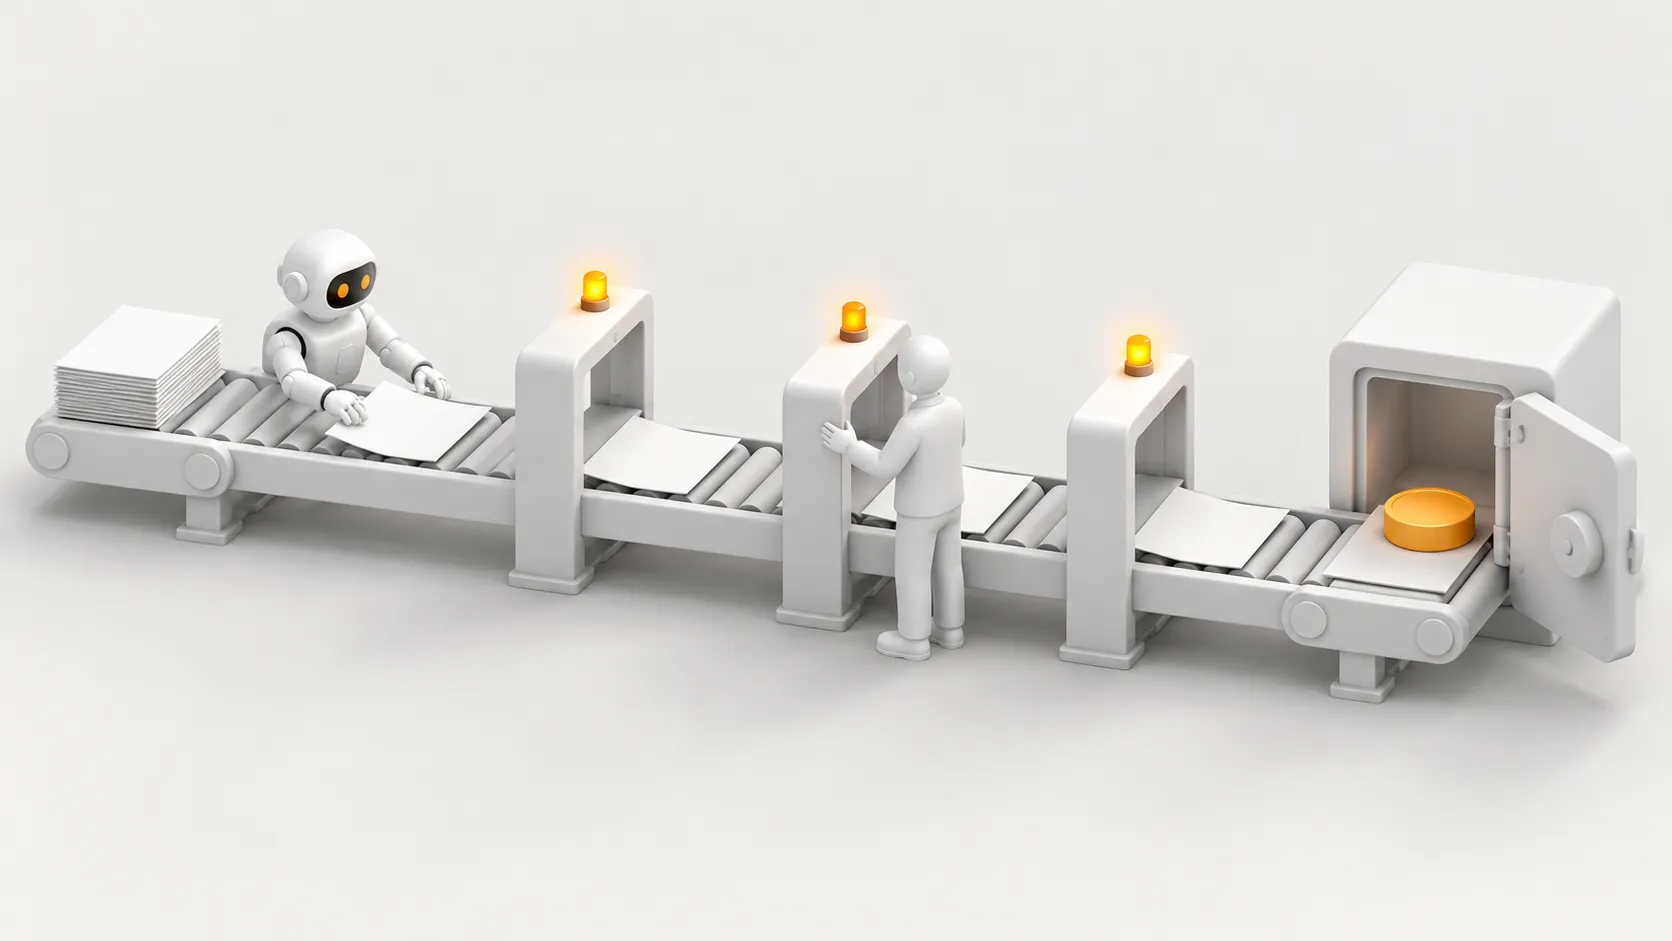
When a company running automated systems finds an agent acting beyond its authorized scope, it needs tiered responses based on impact. A minor read-only overreach can be handled by revoking a single tool permission and running in a downgraded state. High-risk writes or external actions call for an immediate stop and frozen credentials, and the security lead decides on recovery after finding the root cause.